Author: anonymousmedia_tal70o

  • US Reportedly Considering Dropping “Mother of All Bombs” on Iran

    US Reportedly Considering Dropping “Mother of All Bombs” on Iran


    By Sharon Zhang

    This article was originally published by Truthout

    The US has only ever dropped a MOAB once before — on Afghanistan in 2017.

    The Pentagon has reportedly drawn up plans to attack Iran with the “Mother of All Bombs” (MOAB), the largest conventional weapon ever developed by weight, after being ordered by President Donald Trump to develop strike plans for targets that include “a lot of energy infrastructure.”

    Energy infrastructure is largely considered to be civilian in nature and thus protected under international law. 

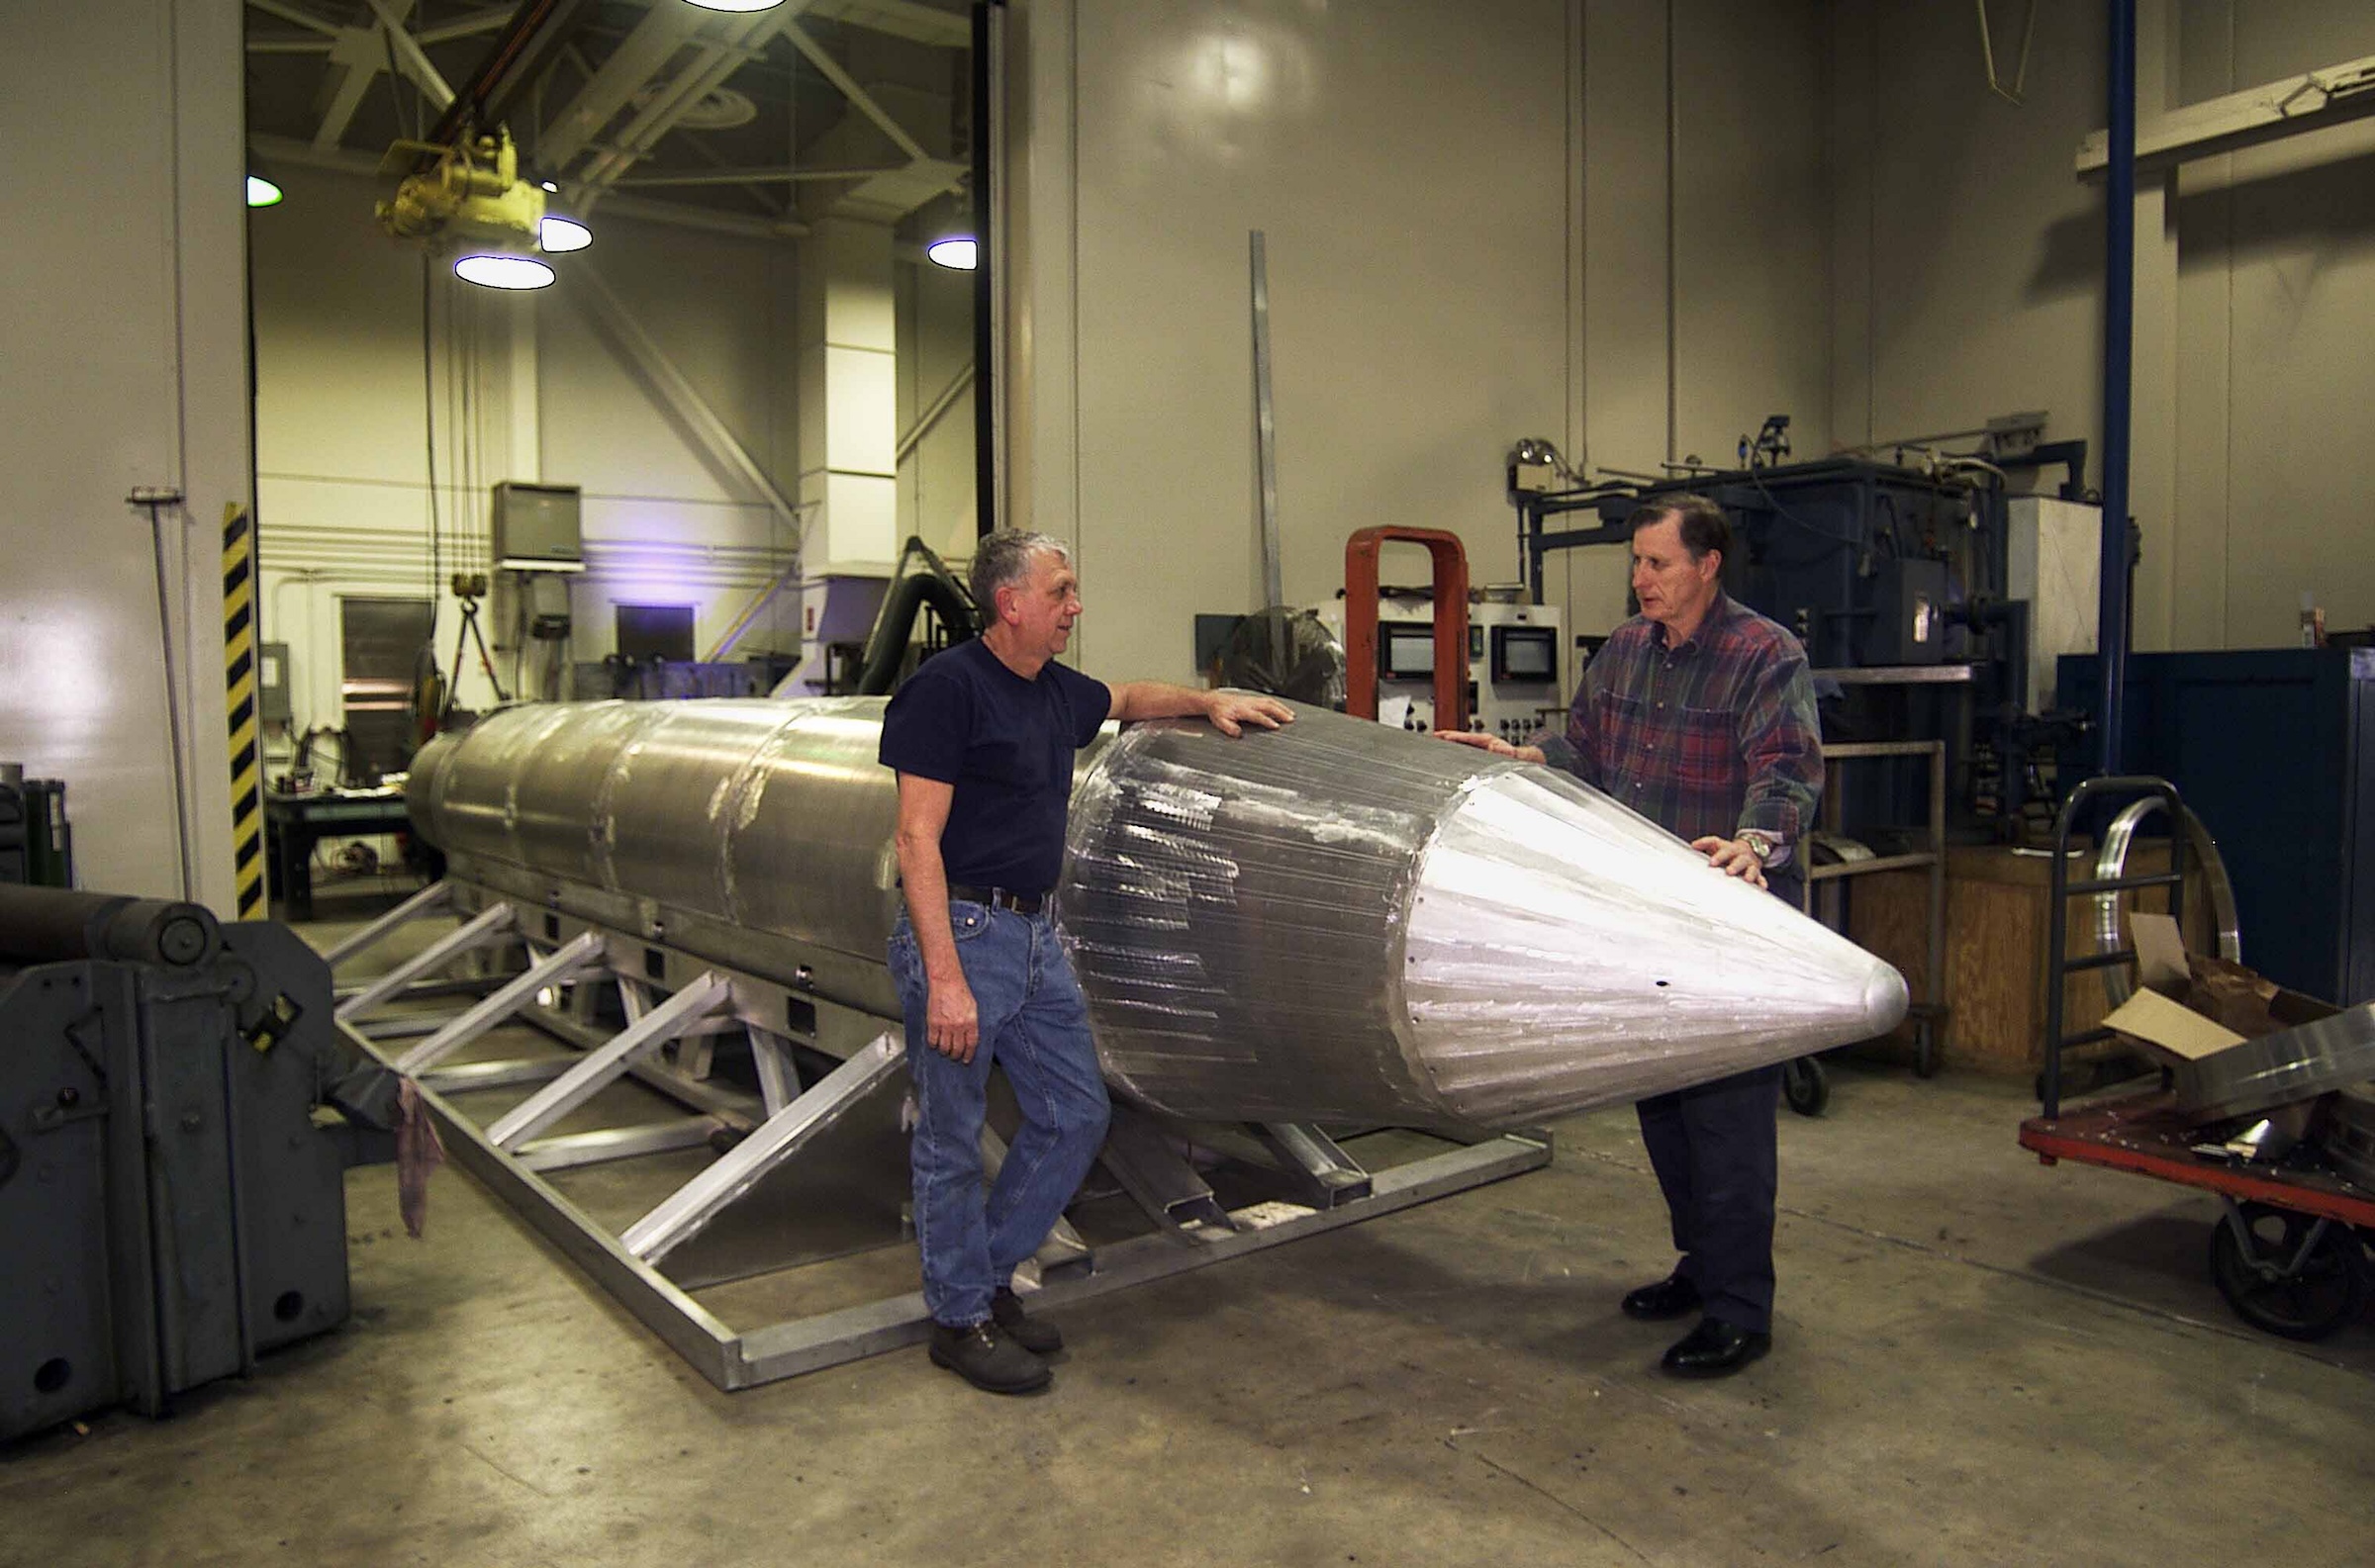
    The GBU-43/B Massive Ordnance Air Blast bomb, or MOAB, is the U.S.’s largest non-nuclear bomb. It is designed to explode a few feet before hitting the ground, creating a massive blast and shooting out plumes of fire, destroying everything within a 0.6 mile radius and causing damage within one mile. It is not an effective weapon against targets like Iran’s highly fortified nuclear infrastructure, experts said, because it does not penetrate deep below ground. 

    Legal experts have previously raised concerns about disproportionate harm to civilians in the U.S.’s use of 2,000-pound bombs on Iran. The MOAB, by contrast, weighs 21,000 pounds, and has a much larger blast radius. 

    The MOAB options were first reported by CNN and confirmed by CBS. The MOAB was first tested in 2003, as the George W. Bush administration developed its strategy of “shock and awe” in Iraq; as CNN notes, at the time, the Pentagon said it hoped that the mere existence of the MOAB was enough to cause “psychological” damage to the enemy.

    The bomb has only been used once before in combat, by Trump. In 2017, the U.S. dropped a MOAB east of Kabul, in Nangarhar, Afghanistan, a province with a population of 1.5 million people. The Pentagon claimed that more than 94 ISIS members were killed in the attack. No civilian deaths were reported; some reports said that the area had long been evacuated. But some local reports suggested that civilians were harmed, and critics afterward noted that the U.S. had previously never considered using the bomb in Iraq because of civilian damage concerns. It caused a mushroom cloud visible from 20 miles away.

    It is unclear what the timing of such an attack on Iran would be. Trump has said that he won’t relaunch strikes against Iran before the midterms, but reports have also said that his administration has drawn up plans to do just that. CNN said advisers privately wonder if Trump’s pledges are definitive.

    CNN additionally found that the Trump administration and military planners have spent recent weeks looking for “an off-ramp that gives Trump a ‘symbolic’ win — at minimum — he can try to sell to the American people without preventing a potential diplomatic breakthrough, starting with an agreement to reopen the Strait of Hormuz.” This includes plans that could amount to strikes for a “fireworks show,” after which Trump would declare victory. 

    “The Trump administration’s threats to commit war crimes in Iran cannot be normalized,” said Ryan Costello, policy director for the National Iranian American Council, in response to the MOAB report. “President Trump acts on many of his threats, necessitating more urgent action to bring this illegal war of choice to a definitive end.”

    The Trump administration has already been under fire for killing civilians in Iran, with several attacks having been described as war crimes by UN experts. This includes the February 28 strike on an elementary school in Minab, Iran, which killed 160 people, including 123 children.

    Pentagon officials said in May that their report on the Minab attack, which is the single worst strike on civilians by the U.S. in the 21st century, was nearing conclusion. But Bloomberg reported on Thursday that the Pentagon is planning to withhold the report at least until after the midterm elections next month, and potentially even longer.

    The attempt to withhold information about the U.S.’s conduct in the deeply unpopular war has incensed critics.

    Defense Secretary Pete “Hegseth eliminated staff who prevent civilian casualties, called the rules of engagement safeguarding civilians ‘stupid,’ & now he’s covering up the report on the Minab school strike that killed over 120 children,” said Sen. Chris Van Hollen (D-Maryland). “He needs to be removed from office & we need accountability NOW.”


    This article was originally published by Truthout and is licensed under Creative Commons (CC BY-NC-ND 4.0). Please maintain all links and credits in accordance with our republishing guidelines.


    Source link

  • Citizen Lab Traces Zero-Click Candiru Spyware Infections at Al Jazeera to Targeted Online Ads

    Citizen Lab Traces Zero-Click Candiru Spyware Infections at Al Jazeera to Targeted Online Ads


    Candiru, an Israeli maker of spyware sold to governments, infected devices at the news network Al Jazeera through ordinary online ads, in attacks that needed no click or other action from the user, researchers at the Citizen Lab said Thursday.

    The hidden attack code ran the moment an ad loaded on the screen, and in some cases the ad loaded out of sight, in the background.

    The Citizen Lab, a research group at the University of Toronto, said this is the first public, technical confirmation that mercenary spyware, meaning hacking tools sold to governments, has reached real devices through targeted ads. The method had been described before from leaked company documents, but not shown in a live attack.

    The researchers recovered the spyware itself from one device, but not the exploit that breaks into the browser or app to install it. That first break-in step is described from how the attack was set up, not from captured code.

    How the Attack Worked

    The ads were placed by Discover-Tech, an Israeli company that presents itself as a normal digital advertising firm. Each ad carried a small piece of code that, when the ad loaded, quietly sent the device’s advertising ID and internet address back to a Discover-Tech server, the researchers found.

    That server decided whether the device belonged to a target. If it did, the server sent back attack code for the browser or app to run. If it did not, the server sent nothing. Because the ad itself carried no attack code, the ad networks that delivered it had nothing harmful to detect.

    Cybersecurity

    At Al Jazeera, at least 45 devices were targeted in 2024 and 2025, the Citizen Lab said, and it linked the attacks to Candiru with high confidence. The researchers did not say which government was behind the operation.

    The network gave the researchers its traffic logs. On infected devices, the logs showed the same order each time: first contact with a Discover-Tech ad server, then a Candiru server that screens the device, then a command-and-control server that runs the spyware.

    Al Jazeera also pulled one Windows program file off a compromised device. Its code used the same distinctive techniques as a Candiru tool the Citizen Lab took apart in 2021, which is the basis for the high-confidence link.

    Al Jazeera staff were targeted once before. In 2020, dozens of its journalists’ iPhones were hacked with NSO Group’s Pegasus spyware, in a different operation that used a different method.

    Who Discover-Tech and Candiru Are

    Google and the advertising trade group IAB Europe had both listed Discover-Tech as an approved ad vendor from 2020 until this month. The company was registered in Israel in 2020 and is led by its chief executive, Dekel Boni.

    Candiru is one of the better-known names in the spyware trade. The United States put it on a trade blacklist in 2021 over spyware used to target government officials, journalists, and activists. In 2025, its assets were bought by a U.S. investment firm, Integrity Partners, and moved into a new company, reported to be Integrity Labs, that the sanctions do not cover.

    What the Platforms Did

    After the researchers shared their findings, Google and IAB Europe removed Discover-Tech from their vendor lists in early October, the Citizen Lab said. Google cut off the company’s access to its ad exchanges, Beeswax removed it, Vungle paused its access for a review, and Eskimi blocked its accounts.

    Google told Reuters it had worked with the researchers and removed Discover-Tech “for systematically violating our policies.” IAB Europe said it suspended the company after an audit found policy violations. Comcast, which owns Beeswax, said it acted “following recent activity.”

    Discover-Tech, Candiru’s owners, Al Jazeera, and the Russian ad network Yandex did not respond to Reuters. Discover-Tech’s website was still online on Thursday and said nothing about the findings.

    How Far the Ads Reached

    Discover-Tech’s reach went far beyond Al Jazeera. On one of its platforms, the company placed nearly four billion ad bids between March and June 2026, the Citizen Lab said, and the ads carrying the hidden callback code appeared in about 75,000 phone apps and 120,000 websites.

    Confiant, a U.S. ad-security firm that investigated alongside the Citizen Lab, put Discover-Tech’s traffic at roughly 10 million ads a day.

    Cybersecurity

    The ads turned up on the networks of governments and large institutions, the Citizen Lab said, including NATO, the United Nations, European Union bodies, government offices in about two dozen countries, chipmakers, and news organizations. An ad appearing on a network is not proof that anyone there was infected. It shows only how widely the system could reach.

    Confiant found that the small number of ads it could tie directly to Candiru were low-volume and mostly reached home and mobile internet connections, rather than the sensitive networks themselves.

    What Defenders Can Check

    Both groups published the web addresses and files associated with the operation, so defenders can block them and search their own records. Organizations whose staff may have seen the ads, especially on the networks named in the report, can look for the attack’s order of connections: a device reaching a Discover-Tech ad server, then a Candiru screening server, then a command-and-control server.

    Among the published indicators:

    • SHA-256 (recovered spyware sample): 255869de85e2a171993fc5eb8a556d873a1b8966e040f6f55926f2fa2d595cc8
    • Domain (Discover-Tech ad server): mtrtb[.]com
    • Full list: the indicators in Confiant’s report, including the command-and-control servers.

    Security researchers have warned for years that the ad-buying system could be turned to this use. In December, leaked documents tied the spyware maker Intellexa to a similar ad-based tool called Aladdin, though no live infection through it had been shown.


    Source link

  • ISC Stormcast For Thursday, October 15th, 2026 https://isc.sans.edu/podcastdetail/10138

    ISC Stormcast For Thursday, October 15th, 2026 https://isc.sans.edu/podcastdetail/10138


    (c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.


    Source link