SolarWinds has released security updates to address a high-severity flaw in Access Rights Manager (ARM) that, if successfully exploited, could lead to an unauthenticated remote code execution vulnerability.
The vulnerability, tracked as CVE-2026-28326, is rated 8.8 out of 10.0 on the CVSS scoring system. The issue affects all versions of Access Rights Manager 2026.2 and prior.
“SolarWinds Access Rights Manager was reported to be affected by an unauthenticated remote code execution vulnerability,” SolarWinds said in an advisory released on September 17, 2026. “The issue stems from a hard-coded static key.”
The company credited Armadin security researcher Kai Huang with discovering and reporting the flaw, which has been patched in ARM 2026.2.1. SolarWinds makes no mention of the vulnerability being exploited in the wild.
The development comes nearly two months after the company shipped fixes for a critical flaw impacting Web Help Desk (WHD) (CVE-2026-28323, CVSS score: 9.8) that could result in a SAML authentication bypass when the SAML 2.0 authentication method is enabled.
Another vulnerability relates to a denial-of-service (DoS) vulnerability (CVE-2026-28299, CVSS score: 8.2) that could cause the Web Help Desk server to crash due to insufficient memory. Both issues have been resolved in WHD 2026.2.1.
SolarWinds has also released fixes for 16 flaws impacting Serv-U (CVE-2026-28302, from CVE-2026-28304 through CVE-2026-28317, CVE-2026-28321, CVE-2026-28323) that could lead to privilege escalation, remote code execution, and the creation of administrator accounts.
Identity visibility is a starting point for modern identity security, because stolen and misused credentials are among the most frequently reported initial access vectors in breach research, including Verizon’s annual Data Breach Investigations Report. This article explains what identity visibility means in IAM, why cloud and multicloud environments complicate it, which capabilities matter in identity visibility tools, and how to build a practical program.
What is identity visibility?
Identity visibility is the ability to see every identity in an environment, what it can access, and how that access is actually used at runtime. It combines inventory, entitlement mapping, and behavioral telemetry into one continuous picture instead of a periodic snapshot.
The important distinction is between intent and execution. Identity and access management (IAM) platforms express policy intent: who should have access, under what conditions, and for how long. Applications and infrastructure reveal execution: which credentials authenticated, which permissions were exercised, and which paths were taken.
The space between those two layers is where identity dark matter lives: local application accounts, embedded service credentials, legacy authentication flows, and integrations that were never onboarded into a central identity provider (IdP). That hidden surface is what makes visibility a security problem rather than an administrative one.
Why identity visibility has become a critical IAM challenge
Identity dark matter is rarely an isolated edge case. It is a common byproduct of a decade of SaaS adoption, cloud migration, and automation. When organizations add systems faster than their identity programs can absorb them, the gap between documented access and real access widens.
The expanding identity attack surface
Attackers have adapted to that gap. Instead of deploying malware that endpoint tools are tuned to catch, many intrusions now begin with compromised legitimate credentials used within the permissions those credentials already hold. The resulting activity can closely resemble normal operational behavior.
Drivers of identity attack surface growth
Credential-based intrusion: Phishing, token theft, and session hijacking produce authentication events that resemble normal user behavior in IdP logs.
Machine and non-human identities: Service accounts, API keys, and workload credentials frequently outnumber employee accounts in cloud-heavy environments and often have no expiration.
Application-local accounts: Systems that authenticate outside single sign-on (SSO) may never appear in centralized access reviews.
Agentic AI workloads: Autonomous agents act with delegated permissions across multiple systems, often at a pace and volume that manual review cannot match.
Why traditional IAM reporting falls short
Most IAM reporting describes configuration: group memberships, role assignments, and entitlement catalogs. That data answers what access was granted, but not whether the application enforced it, whether the account still has a human owner, or whether the permission has been used in the last year.
Governance platforms also tend to report on the applications connected to them rather than verify coverage independently. If an application was never integrated, it does not appear in the report, and absence can be mistaken for compliance.
Understanding identity visibility in IAM: core concepts
Verification, not assumption, is the organizing principle behind identity visibility in IAM. Three concepts make that verification possible: accurate inventory, mapped access relationships, and continuous contextual analysis.
Identities, entitlements, and access relationships
An identity inventory lists the actors. An entitlement map explains what each actor can do. Access relationships connect the two across systems, revealing effective permissions rather than nominal ones.
Effective access is often broader than intended. A user assigned a modest application role may inherit administrative capability through a nested group, a shared service account, or a trust relationship between cloud accounts. Relationship mapping exposes those chained paths, and those paths are what attackers traverse during lateral movement.
Continuous discovery and contextual risk analysis
Discovery answers a harder question than inventory: what exists that nobody registered? Continuous discovery pulls identity data directly from applications and infrastructure, surfacing local accounts, embedded credentials, and authentication methods that centralized IAM platforms never recorded.
Context then converts findings into priorities. A dormant account with read access to a test system is low-consequence noise. A non-expiring automation credential with write access to production, no assigned owner, and no multi-factor authentication (MFA) carries materially higher risk.
Cloud identity visibility and the multicloud identity visibility challenge
Context fragments the moment identity data crosses provider boundaries. Cloud identity visibility is difficult not because cloud platforms lack logging, but because each one models identity differently and none of them describes what happens in the others.
Identity silos across cloud providers and SaaS applications
Each platform expresses permissions in its own vocabulary. Multicloud identity visibility is the practice of normalizing those vocabularies so a single identity can be traced across every environment it touches.
Identity models that require normalization
AWS: Roles, identity- and resource-based policies, and cross-account role assumption define what a principal can reach.
Azure/Entra ID: Directory principals, Azure RBAC role assignments, and consented application permissions (delegated and application scopes).
Google Cloud: Service accounts and IAM bindings that inherit scope through the organization, folder, and project hierarchy.
SaaS applications: Proprietary admin tiers, custom roles, and local accounts that never reach the identity provider.
Without normalization, security teams review each platform separately and can miss the connective tissue: federated trust, cross-account assumption, and shared credentials that let an identity in one cloud act inside another. Cloud lateral movement commonly follows these IAM trust relationships rather than network paths.
Human, machine, and nonhuman identities in the cloud
Machine identities are a subset of non-human identities, and in cloud environments they often represent the majority of principals. Infrastructure automation creates them — pipelines, Terraform runs, orchestration tools — rather than HR-driven joiner-mover-leaver events, so they tend to bypass the lifecycle governance built for employees.
Control-plane identities deserve particular attention. Because they configure infrastructure itself, a compromised automation credential can create new access, alter logging configuration, or disable the controls meant to detect it. Every non-human identity benefits from the same governance attributes as a human account: a named owner, a stated purpose, an expiration or rotation schedule, and active monitoring.
Identity visibility tools (IVIP): a list of key capabilities
Monitoring machine and human identities at scale is the job of identity visibility and intelligence platforms (IVIP), a category that emerged because governance, cloud posture, and detection tools each addressed part of the problem. The vendors below approach it from different architectural starting points.
Identity visibility platforms and their primary approaches
The list is illustrative rather than exhaustive, and it is not ordered by performance. Capability sets overlap and change frequently, so evaluate against your own environment and requirements. Note that this page is published by Orchid Security, which appears in the list.
Orchid Security: Discovers identities, entitlements, and authentication flows directly from applications and infrastructure rather than relying only on IAM configuration data, and turns that telemetry into audit-ready compliance evidence. Oriented toward application-layer blind spots.
Veza: Observability-centric access graph that maps effective permissions across data systems, cloud platforms, and SaaS, with an emphasis on entitlement-relationship analysis.
SailPoint: Governance-centric identity security platform focused on lifecycle management, certification campaigns, and policy enforcement at enterprise scale.
Saviynt: Converged governance and cloud entitlement management, combining identity governance and administration (IGA) workflows with cloud infrastructure entitlement management (CIEM) analysis.
Silverfort: Runtime authentication visibility and enforcement, including legacy and unmanaged systems that cannot readily be onboarded to modern SSO.
Semperis: Posture-centric protection for Active Directory and Entra ID, emphasizing configuration hygiene, attack-path analysis, and recovery.
CrowdStrike Falcon Identity Protection: Detection-centric identity threat detection and response (ITDR) tied closely to endpoint and workload telemetry.
Unified identity inventory and access mapping
Whatever the starting architecture, the baseline capability is the same: one authoritative inventory that reconciles identities across IdPs, cloud platforms, applications, and infrastructure, then maps effective access between them.
A useful test of that inventory is whether it includes identities nobody registered. A platform that reads only IAM configuration will reproduce the blind spots already present in IAM. Application-layer discovery separates a report from an inventory.
Risk detection, analytics, and remediation workflows
Inventory without analysis creates a longer list, not a safer environment. Detection quality depends on the behavioral baseline: knowing what normal usage looks like for a given identity before judging a deviation.
Analytics capabilities worth evaluating
Behavioral baselining: Distinguishes routine automation activity from anomalous privilege use by the same credential.
Attack-path analysis: Assesses whether a misconfiguration is exploitable given permissions, reachability, and runtime context.
Technique mapping: Aligns findings to MITRE ATT&CK identity-related techniques, such as Valid Accounts (T1078), so analysts can reason about adversary behavior rather than isolated alerts.
Remediation routing: Sends findings to the owning team with the evidence needed to act, rather than to a shared queue.
How identity visibility and intelligence fits the identity fabric
Identity visibility and intelligence is not a replacement layer. It is the observability layer that makes existing identity investments verifiable.
Connecting IAM, IGA, PAM, and security operations
IAM platforms generally operate in two dimensions: design time, covering lifecycle, policy, and provisioning, and runtime, covering authentication and authorization enforcement. Visibility platforms observe both and report the difference between them.
That reporting feeds each neighboring system differently. IGA receives evidence that certifications reflect real access. Privileged access management (PAM) receives discovery of privileged accounts operating outside vaulting. Security operations receive identity context that can shorten timeline reconstruction during an investigation, instead of requiring analysts to stitch events together across several consoles.
Using identity intelligence to support zero trust
Zero trust, as described in NIST SP 800-207, assumes continuous verification, and continuous verification requires continuous observation. Access decisions are only as good as the signal behind them: session context, credential type, historical behavior, and the sensitivity of the target system.
Identity intelligence supplies that signal. It also supplies the counterweight: evidence of where enforcement is not actually happening, such as applications still accepting legacy authentication protocols or administrative accounts without MFA.
Real-world use cases and implementation best practices
Prioritization is where many programs succeed or stall. Mature organizations tend to treat identity visibility as a maturity journey: from manual, static governance, to automated and continuous control, to behavioral observability across applications and infrastructure.
Prioritizing high-risk identities and excessive privileges
Permission sprawl is a common finding in cloud environments, often because IAM policies were provisioned broadly during deployment and never right-sized afterward. Start where excess privilege intersects with exposure.
Practical first targets include unowned service accounts with production write access, administrative accounts authenticating without MFA, credentials that have never been rotated, and dormant accounts belonging to departed staff. Each is a concrete, fixable finding with a clear owner, which builds credibility for the broader program.
Building a phased identity visibility program
Sequencing matters because discovery generates volume, and volume without a remediation path creates alert fatigue.
Program rollout sequence
Scope definition: Identify the crown-jewel applications and cloud accounts where identity compromise would cause the most damage.
Direct discovery: Pull identity and entitlement data from those applications and infrastructure layers, not only from the IdP.
Effective access mapping: Resolve nested groups, trust relationships, and inherited permissions into real capability.
Ownership assignment: Give every account, including non-human ones, a named human owner and a review or expiration date.
Behavioral monitoring: Baseline normal usage and alert on deviations in privilege use and authentication patterns.
Evidence automation: Generate compliance artifacts from live telemetry rather than reassembling spreadsheets each audit cycle.
Timelines vary widely with environment complexity, application count, and the availability of application owners.
Found this article interesting? This article is a contributed piece from one of our valued partners. Follow us on Google News, Twitter and LinkedIn to read more exclusive content we post.
The report raises questions regarding the military’s line-of-duty investigations following service member deaths.
Support justice-driven, accurate and transparent news — make a quick donation to Truthout today!
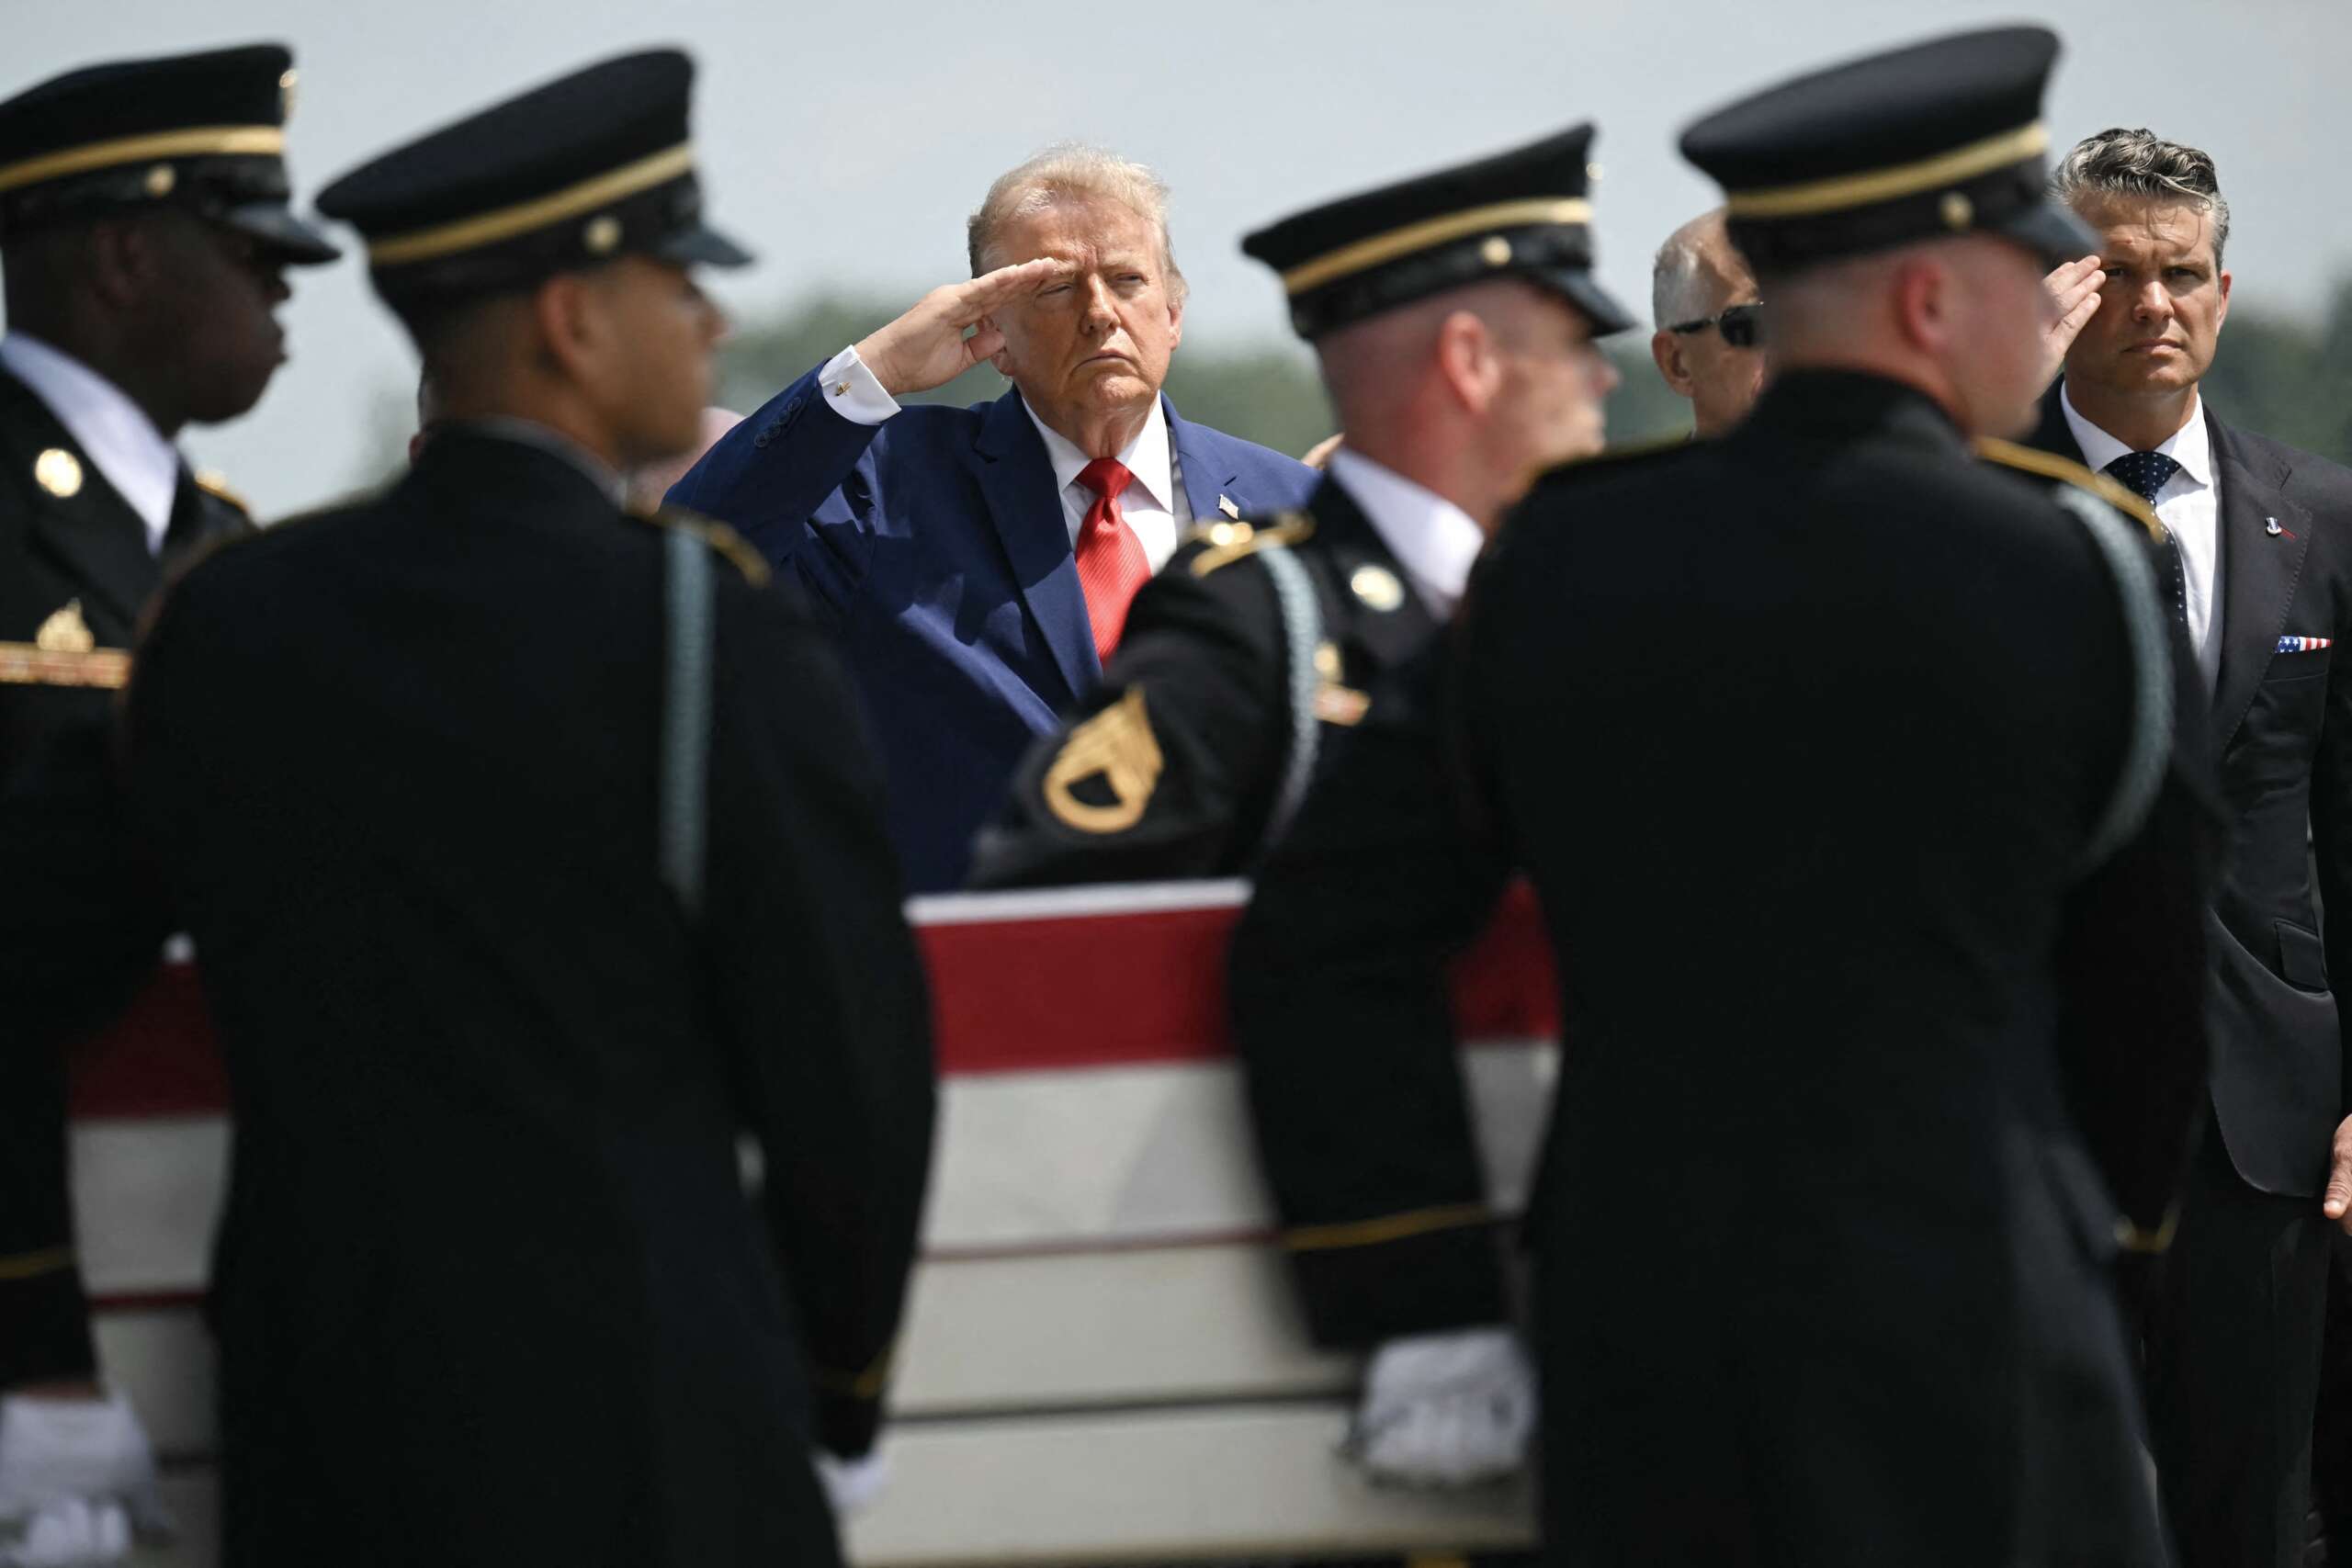
The Trump administration — which calls itself the “most transparent administration in history” — is once again under fire for its lack of transparency after The Washington Post on Friday published a report in which US officials said more American troops have died during the Iran War than the Pentagon has disclosed.
Five officials familiar with the Pentagon’s internal casualty accounting told the Post under condition of anonymity that at least 22 US service members have died since Trump launched the Iran War on February 28 — four more than the 18 fatalities currently listed in the Pentagon’s public Defense Casualty Analysis System, or DCAS. A sixth official put the number at 23.
The officials said that not all of the additional deaths were necessarily caused directly by Iranian attacks, but rather involved US personnel stationed in the Middle East.
The Pentagon says 18 U.S. troops have died in Trump’s Iran war. But new reporting from six U.S. officials with direct access to the Pentagon’s casualty data, says the real number is higher. Five put the toll at at least 22, while one put it at 23.
This isn’t the first time the Pentagon’s counting has come under scrutiny. Earlier this year, four fallen soldiers were reclassified off the official Iran war death toll and into “overseas operations” casualties, because they were killed during Trump’s short-lived ceasefire.
When the government hides the true cost of its war, it misleads the country and dishonors the fallen. Every service member who gives their life deserves to be recognized, anything less is unacceptable.
https://t.co/sWJKjGZzWv
The report raises questions regarding transparency, as well as the military’s line-of-duty investigations following service member deaths that can affect survivors’ benefits.
Retired US Army Brig. Gen. Steve Anderson asked some of those questions in a Friday Substack post directed at Hegseth and calling the reported obfuscation an “unforgivable sin”:
Why are you hiding from the American people and the media?
Why haven’t you done a press conference in the Pentagon for four months?
What were the families of the fallen told about the circumstances around the deaths of their loved ones? Were they denied recognition for their loved ones’ service and sacrifice in war?
Who made the call to hide the number from the American people?
How many more people have been wounded than we know about?
What are [you] going to do to make this right?
Responding on social media to the Post report, US Defense Secretary Pete Hegseth wrote, “This is DISGUSTING and FAKE. A complete LIE.”
“Shame on The Washington Post — they’re worse than Iranian state media,” Hegseth added.
Hegseth’s denial follows earlier controversies over the Pentagon’s casualty reporting.
In July, the department’s public database briefly excluded four US service members killed during renewed fighting, even though the Pentagon had separately announced the deaths. Officials subsequently blamed the discrepancy on technical problems.
Also in July The New York Timesrevealed that the Pentagon hid dozens of US military injuries from Iranian strikes on bases in Jordan.
Sen. Tammy Duckworth (D-Ill.), a disabled Iraq War veteran, wrote on Bluesky in response to the Post report that “22 of our service members have been killed in Trump’s illegal war. Not 18 like we were told.”
“The Pentagon hid four more heroes’ deaths from us for months,” she added. “Congress cannot let them get away with this.”
To that end, Duckworth and other Democratic lawmakers in both the House and Senate have introduced legislation aimed at preventing the Pentagon from manipulating troop casualty data.
Last month, Duckworth led 17 upper chamber colleagues in introducing the Honoring the Sacrifices of Our Troops in War Act, which her office said came partly in response to the Trump administration’s “shameless attempt to downplay the damage done and evade accountability to the American people.”
Outgoing Congressman Thomas Massie (R-Ky.) on Thursday separately moved to force a House vote on impeaching Hegseth, accusing the defense secretary of violating provisions of the War Powers Resolution by continuing hostilities without congressional authorization.
After several failed attempts, both houses of Congress in June passed a war powers resolution directing Trump to withdraw US forces from hostilities with Iran. Trump did not comply.
The number of US troops killed and wounded in the Iran War pales in comparison to Iranian casualty figures. Thousands of Iranians — including more than 3,500 civilians, more than 380 of them children — have been killed and tens of thousands more wounded by US and Israeli attacks since February 28, according to Iranian and international officials.
25 Years of Truthout: An important fundraising appeal
This September, Truthout is celebrating 25 years of publication. For over two decades, we have been a trusted source for fiercely independent journalism thanks to readers like you.
As we look to the next 25 years, we have launched a special fundraising campaign. Looking to a sustainable future for our publication, we have a fundraising goal of $71,000 in the next 5 days.
We are asking for your support at this juncture because we face greater threats than ever before in our organizational history. Trump and his MAGA allies are determined to control the information ecosystem, and movement-based organizations are subject to dangerous censorship and scrutiny.
If you can support Truthout with a one-time or monthly donation, you will make a significant impact on our work and our legacy. Anything you can do makes a difference!