Author: anonymousmedia_tal70o

  • PEERSTITCH Malware Deployed via FortiOS Flaw Bypasses Checks on Tagged VPN Sessions

    PEERSTITCH Malware Deployed via FortiOS Flaw Bypasses Checks on Tagged VPN Sessions


    A suspected advanced threat actor has been observed exploiting a security flaw in Fortinet FortiOS to deliver a previously unreported memory-resident ARM64 malware known as PEERSTITCH.

    The attack involves the exploitation of CVE-2025-61624 (CVSS score: 5.4), a path traversal flaw in the command line interpreter of FortiOS, FortiPAM, FortiProxy, and FortiSwitchManager that could allow a privileged attacker to achieve arbitrary write or delete files via specifically crafted arguments to existing commands. It was patched by Fortinet in April 2026.

    “PEERSTITCH leaves no persistent binary on disk, opens no listening ports and initiates no outbound network connections,” Palo Alto Networks Unit 42 researchers Daniel Gott and Shawn Westfall said. “Instead, it communicates through traffic generated by legitimate processes on the infected host, which makes the malware resistant to conventional endpoint and network detection.”

    The cybersecurity company said it discovered the activity as part of its prolonged network intrusion against a telecommunications managed service provider that took place in September 2024. The multi-stage network intrusion is being tracked as CL-STA-0954 (aka UNC5820), with initial access obtained by exploiting a critical Fortinet FortiManager flaw dubbed FortiJump (CVE-2024-47575).

    Cybersecurity

    Following a successful compromise of the appliance, the attackers are said to have exfiltrated an archive containing running configurations, cryptographic material, and database files containing information about more than 500 managed FortiGate firewalls. Some of the harvested details are listed below –

    • The FortiManager appliance’s own serial number and its management relationships to every enrolled device
    • Running configuration files for more than 500 managed FortiGate firewalls across internal infrastructure and client networks
    • Central management SQLite databases
    • An inventory listing more than 500 FortiGate serial numbers alongside their respective public IP addresses
    • Internal network topology maps, routing tables and interface configurations
    • Ciphertext administrative, local, and SSL/VPN credentials
    • Encoded cryptographic trust material, including public certificates, and private keys

    The stolen information was then used to conduct network reconnaissance, establish long-term access, intercept network traffic, set up unauthorized FortiGate SSL/VPN sessions to perimeter firewalls, deploy backdoors, and exploit a separate privilege-escalation vulnerability (i.e., CVE-2025-61624) to deploy PEERSTITCH.

    The malware is a 64-bit Linux ARM64 executable written in C. It includes an auto-script designed to download five components from an external server (“23.240.77[.]233:8085”) –

    • pM.js, an environment preparation script (self-deleting)
    • a.js (saved as index.js), an Emscripten JavaScript runtime module
    • a.wasm (saved as index.wasm), a compiled WebAssembly binary module
    • b.js (saved as ipssem.js), a deployment orchestrator script
    • dd (saved as lldprx), a native ARM64 ELF binary injector (PEERSTITCH core)

    The main phase of the attack begins after an execution delay. The orchestrator (“ipssem.js”) launches “lldprx,” which then serves as a process memory patching injector targeting two core FortiOS daemons: “/bin/miglogd” and “/bin/iked.”

    Specifically, it locates the running processes associated with the two daemons, enumerates their memory layout, attaches to them using ptrace and halts their execution using PTRACE_INTERRUPT, allocates executable memory and writes malicious code into it, and redirects execution through the injected code.

    The end goal behind this hooking step is to create a “covert, memory-resident communication bridge” between the two legitimate FortiOS processes instead of using a conventional network connection or file, and use them as a cover to sidestep detection.

    Specifically, the miglogd hook is equipped to recognize a marker in the data it is passing through the process. This includes two specific markers –

    • TCP port marker – 8550 (embedded within traffic data, not a listening port)
    • IP address marker – 169.254.0.1 (link-local identifier used for pattern matching)

    Once this pattern is identified, it passes the associated session token or identifier to the iked daemon, whose hook later looks for that identifier while handling subsequent VPN sessions. If such a tag exists within that VPN session’s injection buffer, it takes an alternative execution path, bypassing default FortiOS security validations.

    Put differently, the hooks injected into the two FortiOS processes change how the VPN daemon handles particular sessions.

    Besides deploying PEERSTITCH, the attackers have been observed establishing a separate command-and-control (C2) channel by leveraging the native Apache “mod_md” module on FortiGate firewalls in order to spawn an SSH-based reverse shell.

    Cybersecurity

    “The attackers also impersonated the FortiManager platform to pull from managed firewalls of other hosts in the targeted network,” the researchers said. “The attackers demonstrated proficiency in Fortinet appliance architecture, FortiOS internals and FortiOS management protocols.”

    Although not definitive, it’s suspected that the attackers may have exploited other flaws like CVE-2024-26009 and CVE-2024-26008 to carry out this task. However, Unit 42 emphasized that exploiting these vulnerabilities requires the device to be enrolled in FortiGate Cloud/FortiCloud SSO, which none of the affected firewalls held.

    In addition, CL-STA-0954 has been identified as undertaking various measures to remove forensic artifacts through termination of syslog generation, crash log clearing, logging telemetry disruption, and automatic deletion of rogue administrator accounts and auto-script objects after execution.

    “This intrusion highlights a growing threat, the weaponization of centralized edge management ecosystems to compromise downstream networks,” Unit 42 said. “The discovery of the PEERSTITCH implant demonstrates the increasing technical maturity of edge-device malware.”

    “By operating as a one-shot injector, avoiding persistent disk artifacts and building a covert inter-process communication bridge inside process memory, the attackers achieved sustained persistence while evading traditional monitoring.”

    Source link

  • Critical PwnEscape Linux Kernel Vulnerability Lets Guest VMs Read Host Memory

    Critical PwnEscape Linux Kernel Vulnerability Lets Guest VMs Read Host Memory


    A newly disclosed critical flaw in the Linux kernel allows code inside a virtual machine to read memory on the host computer it runs on. A researcher demonstrated the leak against Vercel’s live cloud sandboxes, and Vercel confirmed it.

    The flaw, now tracked as CVE-2026-99999 and nicknamed PwnEscape, is in the Linux kernel’s networking code, not in any one cloud’s setup, so it reaches the shared layer that cloud providers use to keep customers’ workloads apart.

    It was found in a Vercel security challenge and reported privately before any public release, and there is no sign it has been used in a real attack.

    What the Researcher Showed

    Paulos Yibelo of the security firm pwn.ai found that specially made network packets sent from inside a virtual machine could do three things, he explained in a technical write-up: read the host’s memory, crash the host, and run code on it. All three come from the same kernel flaw.

    Vercel said in its report on the challenge that the memory leak was demonstrated against its production sandboxes. Each packet the guest sent out could carry back about 32 bytes of the host’s memory, and the guest could keep going as long as it kept sending packets.

    The crash and code execution were observed only on the researcher’s own machines, which were set up to match Vercel’s. Two specially crafted packets were enough to crash a host and take down every sandbox running on it.

    Cybersecurity

    Using the same flaw, the researcher then reached administrator control of a host, breaking out of the virtual machine. He stressed this was a lab result, “not a claim of root command execution in any vendor’s production environment.”

    “Our research ran through Omega-Pwn, an internal harness combining our own security research tooling with elements of SingularityNET’s OmegaClaw architecture. It let us carry hypotheses, code traces, failed attempts, and experimental results across long-running research sessions. GPT-5.6 Sol was the primary reasoning engine. We directed the investigation, challenged its findings, and validated the interesting ones against actual kernel behavior on systems we controlled,” Paulos Yibelo told The Hacker News.

    Vercel said no report in the challenge showed anyone reading a customer’s files, secrets, or application data.

    How Severe It Is, and Who Can Set It Off

    The kernel’s maintainers assigned the flaw CVE-2026-99999 and, in the published record, rated it 9.3 out of 10, or Critical. The U.S. National Vulnerability Database had received that entry but had not yet finished its own review.

    The same record lists the attack vector as local. In plain terms, the attacker has to already be running code inside a guest, as the researcher was. This is not a flaw that an outsider can exploit by sending packets across the open internet.

    It is not in CISA’s catalog of actively exploited vulnerabilities, and no real-world use has been reported.

    Why It Reaches Beyond Vercel

    Vercel Sandbox runs each customer’s code in its own Firecracker microVM, a small virtual machine with its own copy of the Linux kernel, on bare-metal Amazon EC2 hosts. That microVM is the wall between one customer and the host, and between one customer and another.

    The flaw is not in that wall. It is in the Linux kernel’s networking code, which the host runs. pwn.ai said Vercel’s sandbox was already hardened beyond normal industry standards, with no misconfiguration it could find.

    Because almost every large cloud separates customer workloads on the same layer of the Linux kernel, Vercel said that a flaw there poses a risk to shared infrastructure rather than to any one provider.

    The Fix and the Fixed Versions

    The fix is a single Linux kernel change, commit 6785011f8b16, written by Red Hat’s Michael S. Tsirkin and merged into the mainline kernel. It adds a check that a packet’s checksum data cannot point into the IPv4 header before the kernel acts on it, and applies that check at five places in the networking code.

    The change is deliberately partial. Its author calls it “a defence in depth measure” and notes that a fuller check on the way packets enter the kernel still needs work.

    The maintainers backported the fix to the stable kernel branches. According to the CVE record, these are the first fixed versions in each supported branch:

    Stable branch First fixed version
    5.10 5.10.272
    5.15 5.15.223
    6.1 6.1.190
    6.6 6.6.159
    6.12 6.12.113
    6.18 6.18.57
    7.2 7.2.11

    Linux distributions ship their own kernels and often add this kind of fix without changing the version number, so check your distribution’s advisory and whether the fix is in the kernel the host is actually running, not only the number from uname.

    Cybersecurity

    What to Do

    Update the host kernel to one of the fixed versions above, or to the vendor build that includes the fix, and reboot into it. Updating only a guest’s kernel does not fix the host. The sources give no separate workaround for this flaw if you cannot update yet.

    Where patching has to wait, the usual step is to limit what a break-in could reach. Vercel said it keeps host kernels up to date, disables nested virtualization, and runs each microVM under Firecracker’s jailer, which grants the microVM process only the permissions it needs. That does not fix the flaw, but it narrows what an attacker who used it could do.

    Found in a $1 Million Challenge

    The flaw was found in a two-week challenge Vercel ran in August that offered up to $1 million in total to anyone who could break out of its sandbox. No single payout reached that figure. The top reward per report was $50,000; Vercel paid $242,000 across 1,285 reports, and this flaw was the one Critical finding.

    pwn.ai said it found the flaw in three days using its own AI-assisted research system, with the model doing the source-code analysis and human researchers directing the work. The firm put the cost at under $700 in API tokens. It was the latest case of researchers using a large language model to help find and chain real flaws, after a separate team used one earlier this year to reach internal systems at OpenAI.


    Source link

  • US Reportedly Considering Dropping “Mother of All Bombs” on Iran

    US Reportedly Considering Dropping “Mother of All Bombs” on Iran


    By Sharon Zhang

    This article was originally published by Truthout

    The US has only ever dropped a MOAB once before — on Afghanistan in 2017.

    The Pentagon has reportedly drawn up plans to attack Iran with the “Mother of All Bombs” (MOAB), the largest conventional weapon ever developed by weight, after being ordered by President Donald Trump to develop strike plans for targets that include “a lot of energy infrastructure.”

    Energy infrastructure is largely considered to be civilian in nature and thus protected under international law. 

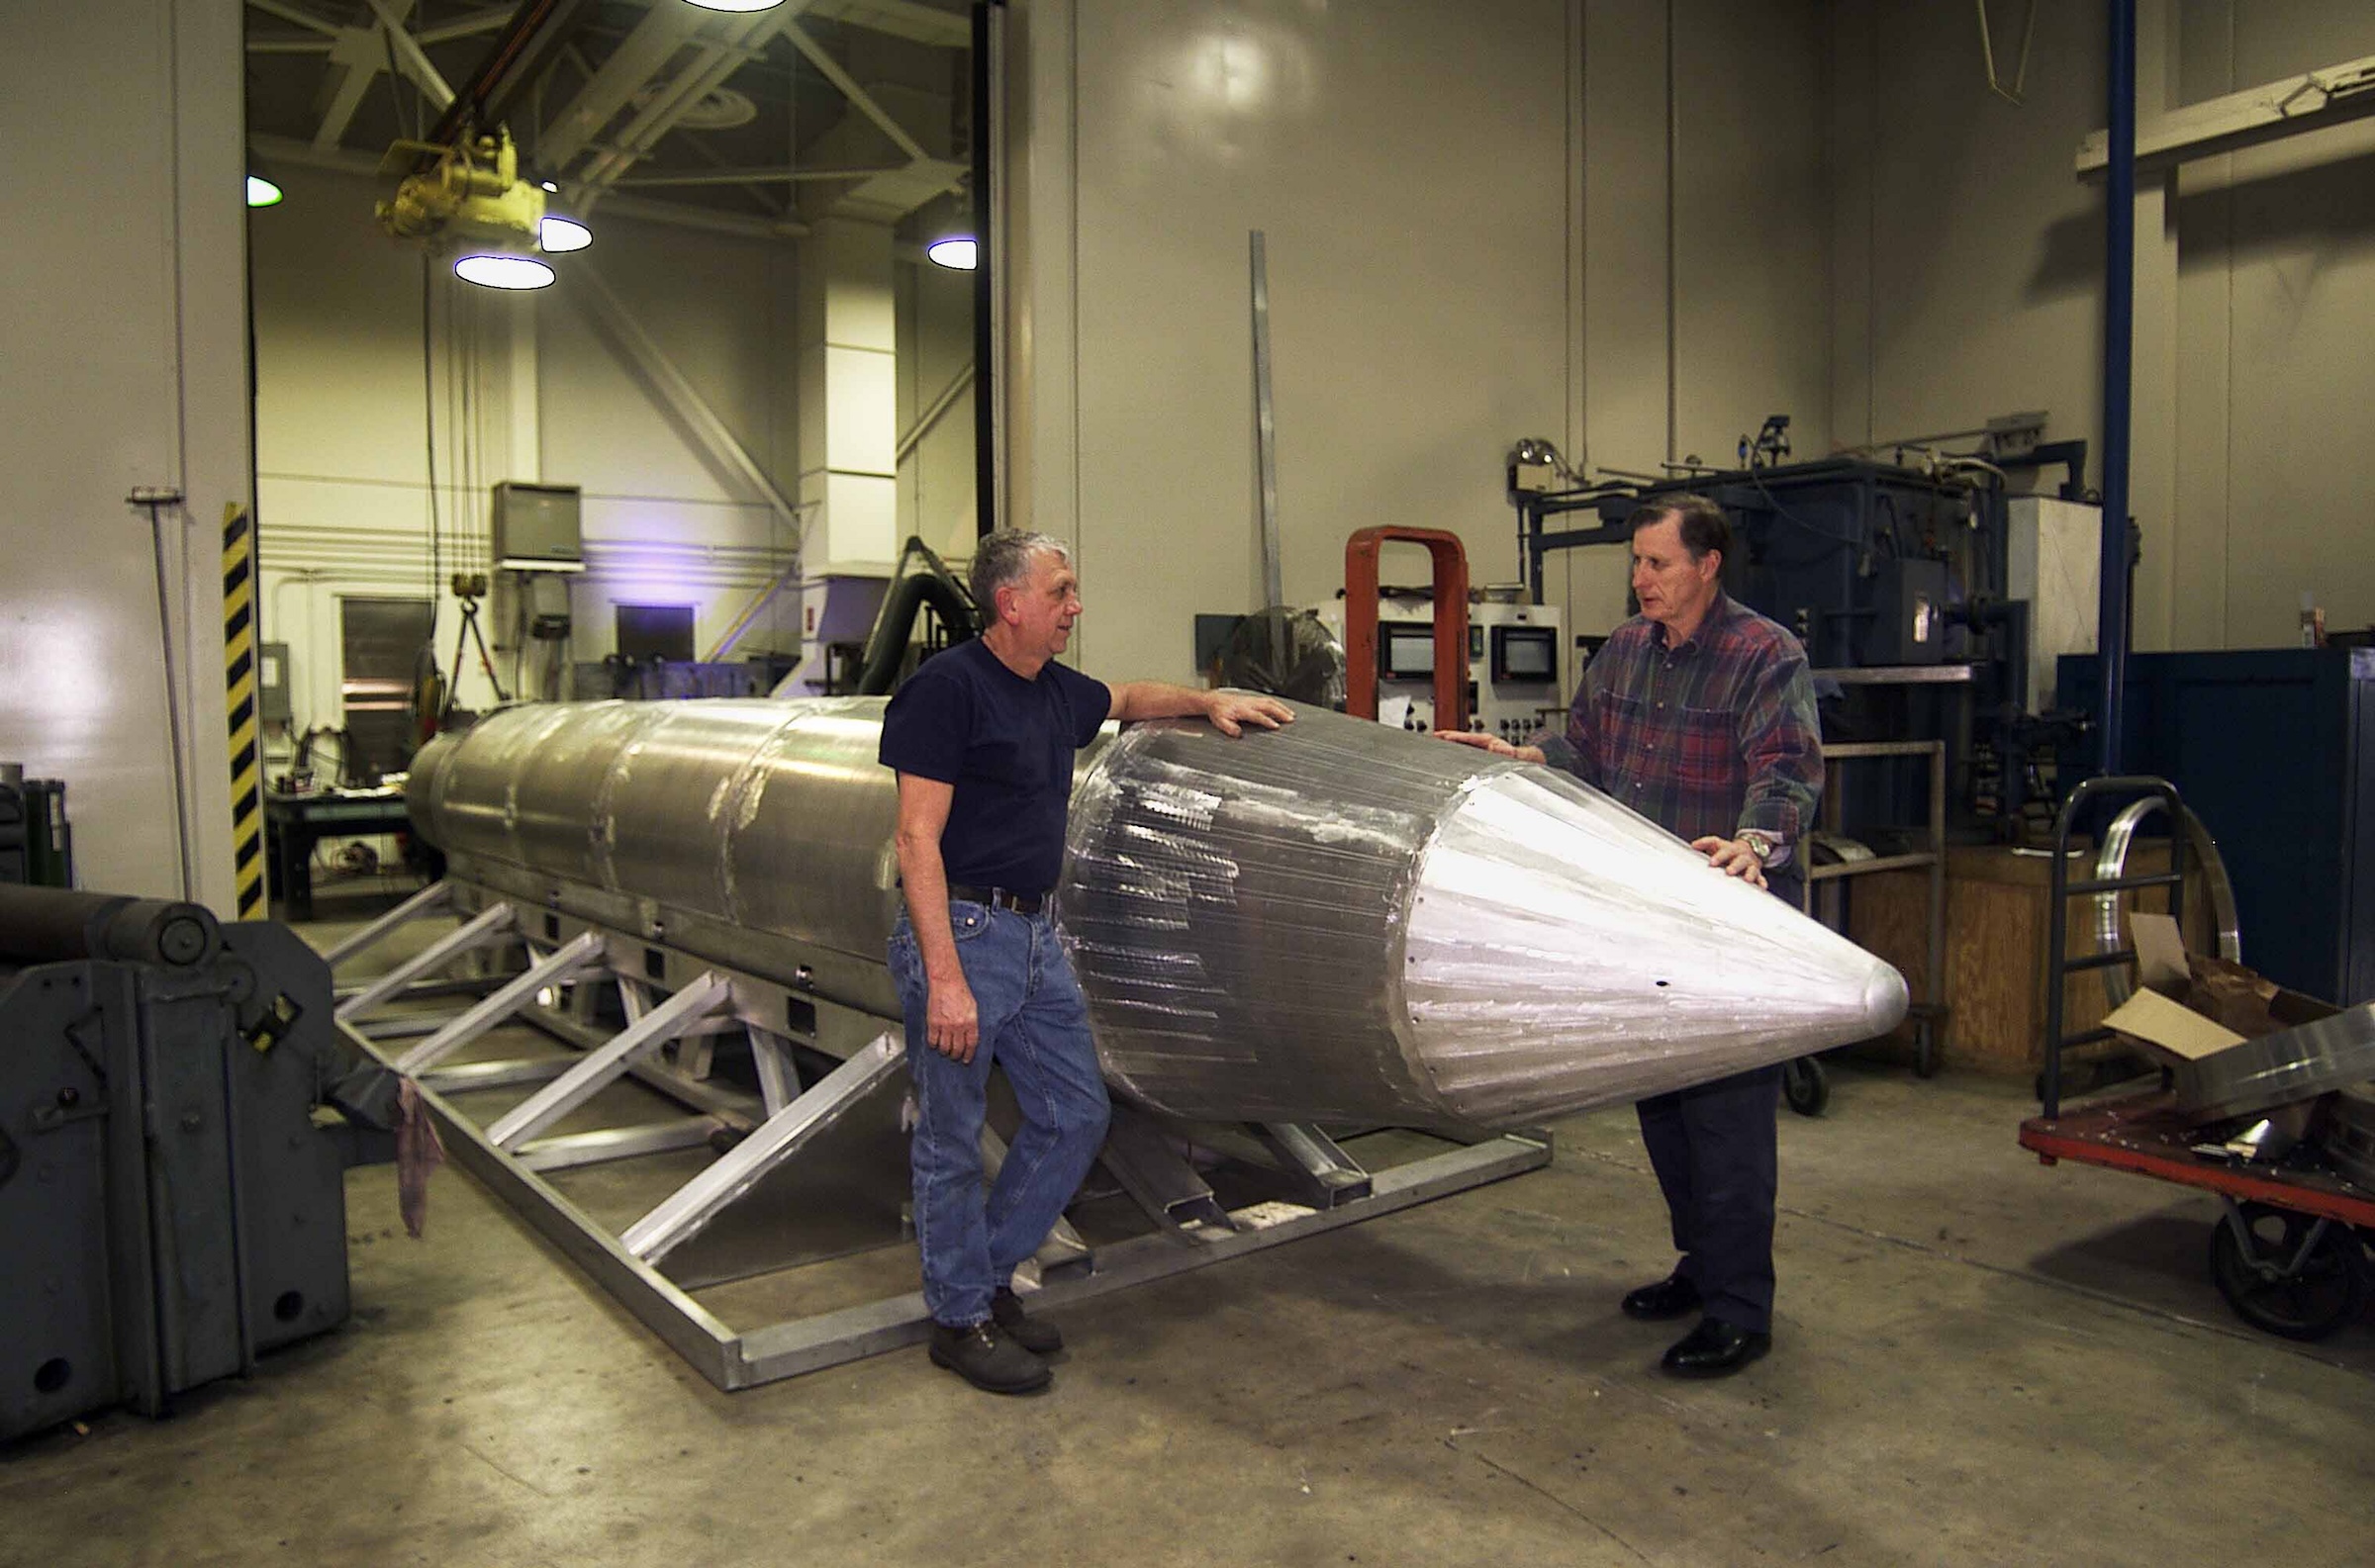
    The GBU-43/B Massive Ordnance Air Blast bomb, or MOAB, is the U.S.’s largest non-nuclear bomb. It is designed to explode a few feet before hitting the ground, creating a massive blast and shooting out plumes of fire, destroying everything within a 0.6 mile radius and causing damage within one mile. It is not an effective weapon against targets like Iran’s highly fortified nuclear infrastructure, experts said, because it does not penetrate deep below ground. 

    Legal experts have previously raised concerns about disproportionate harm to civilians in the U.S.’s use of 2,000-pound bombs on Iran. The MOAB, by contrast, weighs 21,000 pounds, and has a much larger blast radius. 

    The MOAB options were first reported by CNN and confirmed by CBS. The MOAB was first tested in 2003, as the George W. Bush administration developed its strategy of “shock and awe” in Iraq; as CNN notes, at the time, the Pentagon said it hoped that the mere existence of the MOAB was enough to cause “psychological” damage to the enemy.

    The bomb has only been used once before in combat, by Trump. In 2017, the U.S. dropped a MOAB east of Kabul, in Nangarhar, Afghanistan, a province with a population of 1.5 million people. The Pentagon claimed that more than 94 ISIS members were killed in the attack. No civilian deaths were reported; some reports said that the area had long been evacuated. But some local reports suggested that civilians were harmed, and critics afterward noted that the U.S. had previously never considered using the bomb in Iraq because of civilian damage concerns. It caused a mushroom cloud visible from 20 miles away.

    It is unclear what the timing of such an attack on Iran would be. Trump has said that he won’t relaunch strikes against Iran before the midterms, but reports have also said that his administration has drawn up plans to do just that. CNN said advisers privately wonder if Trump’s pledges are definitive.

    CNN additionally found that the Trump administration and military planners have spent recent weeks looking for “an off-ramp that gives Trump a ‘symbolic’ win — at minimum — he can try to sell to the American people without preventing a potential diplomatic breakthrough, starting with an agreement to reopen the Strait of Hormuz.” This includes plans that could amount to strikes for a “fireworks show,” after which Trump would declare victory. 

    “The Trump administration’s threats to commit war crimes in Iran cannot be normalized,” said Ryan Costello, policy director for the National Iranian American Council, in response to the MOAB report. “President Trump acts on many of his threats, necessitating more urgent action to bring this illegal war of choice to a definitive end.”

    The Trump administration has already been under fire for killing civilians in Iran, with several attacks having been described as war crimes by UN experts. This includes the February 28 strike on an elementary school in Minab, Iran, which killed 160 people, including 123 children.

    Pentagon officials said in May that their report on the Minab attack, which is the single worst strike on civilians by the U.S. in the 21st century, was nearing conclusion. But Bloomberg reported on Thursday that the Pentagon is planning to withhold the report at least until after the midterm elections next month, and potentially even longer.

    The attempt to withhold information about the U.S.’s conduct in the deeply unpopular war has incensed critics.

    Defense Secretary Pete “Hegseth eliminated staff who prevent civilian casualties, called the rules of engagement safeguarding civilians ‘stupid,’ & now he’s covering up the report on the Minab school strike that killed over 120 children,” said Sen. Chris Van Hollen (D-Maryland). “He needs to be removed from office & we need accountability NOW.”


    This article was originally published by Truthout and is licensed under Creative Commons (CC BY-NC-ND 4.0). Please maintain all links and credits in accordance with our republishing guidelines.


    Source link