Category: Uncategorized

  • Orphaned VBA Projects Inside DWG Files, (Wed, Oct 14th)

    Orphaned VBA Projects Inside DWG Files, (Wed, Oct 14th)


    Years ago I wrote diary entries about VBA code stored inside AutoCAD drawing files (.dwg).

    In a nutshell: the VBA code is stored inside an OLE file, that is embedded inside the DWG file. You can do a brute-force search for the embedded OLE file, or you can follow a pointer inside the header of the DWG file.

    I wrote a small Python script (autocad.py) for this second case. It looks at a 32-bit pointer at position 0x24 inside the DWG file. This points to a 16-byte long header, followed by the embedded file. This 16-byte long header contains the length of the embedded file. You use the script together with my tool cut-bytes.py, like this:

    cut-bytes.py -S autocad.py -P AutoCAD : 461ed52aeb75384133a8238b2eb481ae5d505d4961effa622673d65a889c8218.vir.zip | oledump.py
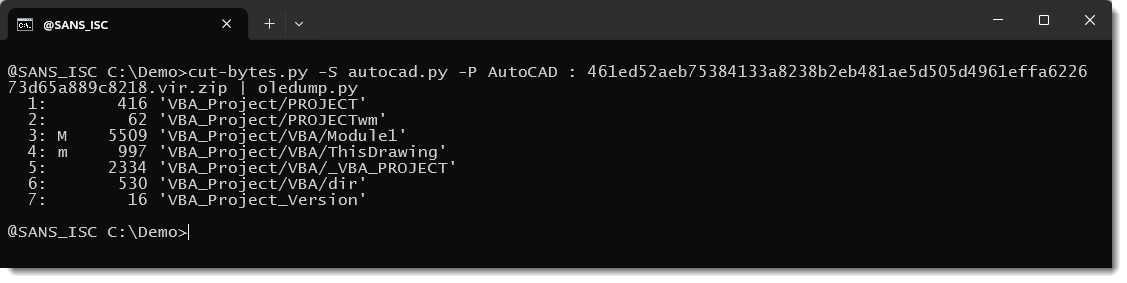
    This command carves the DWG file (inside the ZIP file) and extracts the embedded OLE file, and pipes it into oledump.py for analysis.

    When the pointer is zero, there is no embedded OLE file, and cut-bytes.py returns nothing.

    Recently, I discovered 2 DWG files that are an exception: their pointer to the embedded OLE file is zero, but if you do a brute-force search, you will find an embedded OLE file with a VBA project.

    For example this DWG file.

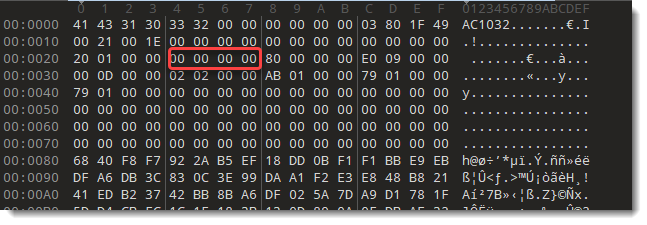
    Its pointer to the embedded VBA project is zero:
    But it contains an embedded OLE file:
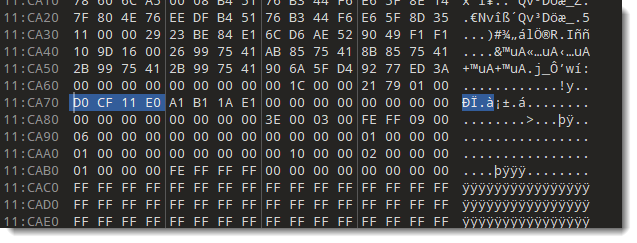
    And right in front of the embedded OLE file, there is the 16-byte long header that contains the lenght of the embedded file.

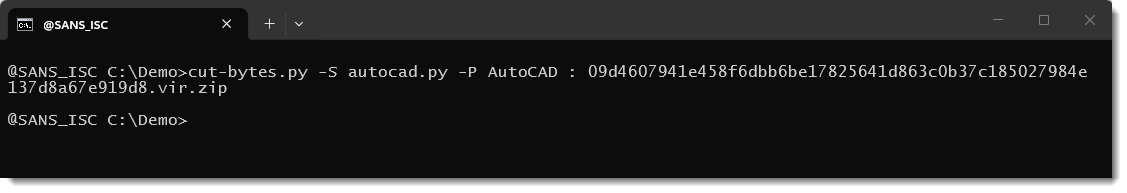
    Using the AutoCAD script to extract the file gives nothing:
    But oledump.py can find the embedded OLE file and analyze it:
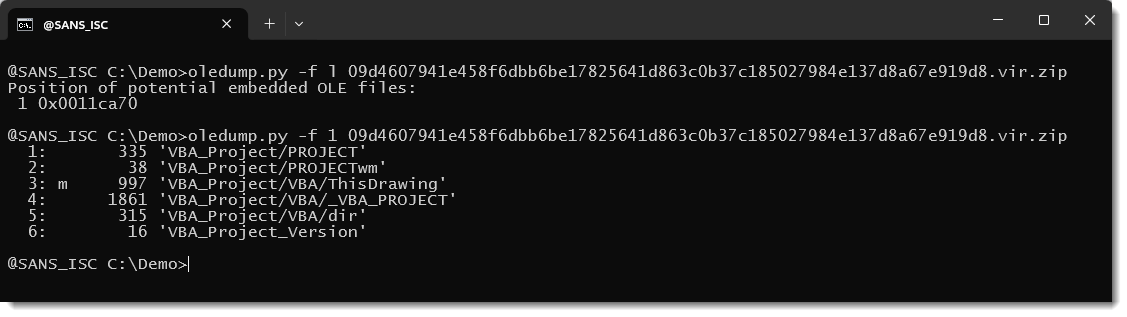
    So while using oledump.py to analyze DWG files you find a VBA project embedded inside a DWG file, then also verify if it is not orphaned: verify that the pointer at 0x24 is not zero (or use the autocad.py script).

    Because when a DWG file contains an orphaned VBA project, the VBA code can not have executed when someone opened the DWG file with AutoCAD. AutoCAD "does not see" orphaned VBA projects.

    Notice that a default installation of AutoCAD does not support VBA. VBA for AutoCAD is a separate install.

    I don't know how orphaning happens, but I did find an AutoLISP command to remove a VBA project from a DWG file: 

    (dictremove (namedobjdict) "ACAD_VBA")

    Maybe this dictremove command clears the pointer, but does not remove the embedded OLE file.

    Didier Stevens
    Senior handler
    blog.DidierStevens.com

    (c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.


    Source link

  • ISC Stormcast For Wednesday, October 14th, 2026 https://isc.sans.edu/podcastdetail/10136

    ISC Stormcast For Wednesday, October 14th, 2026 https://isc.sans.edu/podcastdetail/10136


    (c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.


    Source link

  • Anthropic Warns Small AI Models Could Soon Form Self-Propagating IoT Botnets

    Anthropic Warns Small AI Models Could Soon Form Self-Propagating IoT Botnets


    Ravie LakshmananOct 13, 2026Artificial Intelligence / IoT Security

    Small artificial intelligence (AI) models may be months away from developing capabilities to self-replicate on IoT devices like smart ovens and off-brand Android TV boxes, according to a warning from Anthropic.

    The frontier AI lab said small AI models could form autonomous, self-propagating worm botnets that are “challenging to shut down,” since “there’s no centralized point to shut off.”

    Prior work has demonstrated that AI agents can act like one by scanning their network, executing an exploit, and copying model weights to a target machine across a GPU cluster with an aim to generate tailored attack strategies and use compromised machines as a botnet to run large language models (LLMs) in order to sustain its reasoning and expand in scale.

    “Such an ‘AI worm’ could carry its model weights with it as it reproduces (or re-download them from a public hub), and then run inference directly on compromised hardware,” Anthropic said. “Effectively, the weights would become part of the malware payload.”

    The idea, at a high level, explains how AI models could potentially break into internet-connected devices and use their computing power to run themselves and spread to other devices, without having to rely on expensive data centers all the time. A more powerful model that’s too large to fit into a single device could be split into small chunks and run across multiple machines to collectively run it.

    Cybersecurity

    A threat actor could build a distributed LLM botnet from poorly secured IoT devices, making it powerful enough to run a capable model. Some of the ways an AI worm could propagate include –

    A fleet of 15 Smart TV boxes running distributed inference of Gemma4-26B-A4B.

    In its test of 11 open-weights models from Alibaba, DeepSeek, Google, Meta MoonShot AI, OpenAI, and Zhipu AI (aka Z.ai), Anthropic said it found GLM-5.2 to be the only model to propagate Llama3.1-8B reliably to 8/8 nodes running the redroid Android emulator in 4 out of 5 trials.

    It also revealed that an AI IoT worm powered by inexpensive Android TV boxes could be a “slow, distributed” system that can produce a meaningful amount of AI computation when a fleet comprising hundreds of thousands of such devices is networked together to run an inference engine.

    Cybersecurity

    Alternatively, it could take the form of a potent cyber model capable of breaching data centers at a high pace, or a model that scams people for compute credits.

    “We don’t yet have a full rogue replicator, but agents are becoming increasingly capable of completing the individual steps in the replication chain (and passing on their adaptations to future copies of themselves),” Anthropic said.

    “We expect AI botnets to infect more than IoT devices, and to use weight-based replication as just one strategy in their playbook. AI botnets could also act intelligently to counter defenders, but we haven’t tested this.”


    Source link